Sometimes, to fix an important security issue, miHosting must temporarily stop one of its servers. This can interrupt the services hosted on it, but it allows us to apply measures that reduce exposure to a vulnerability and restore service with the fix in place.
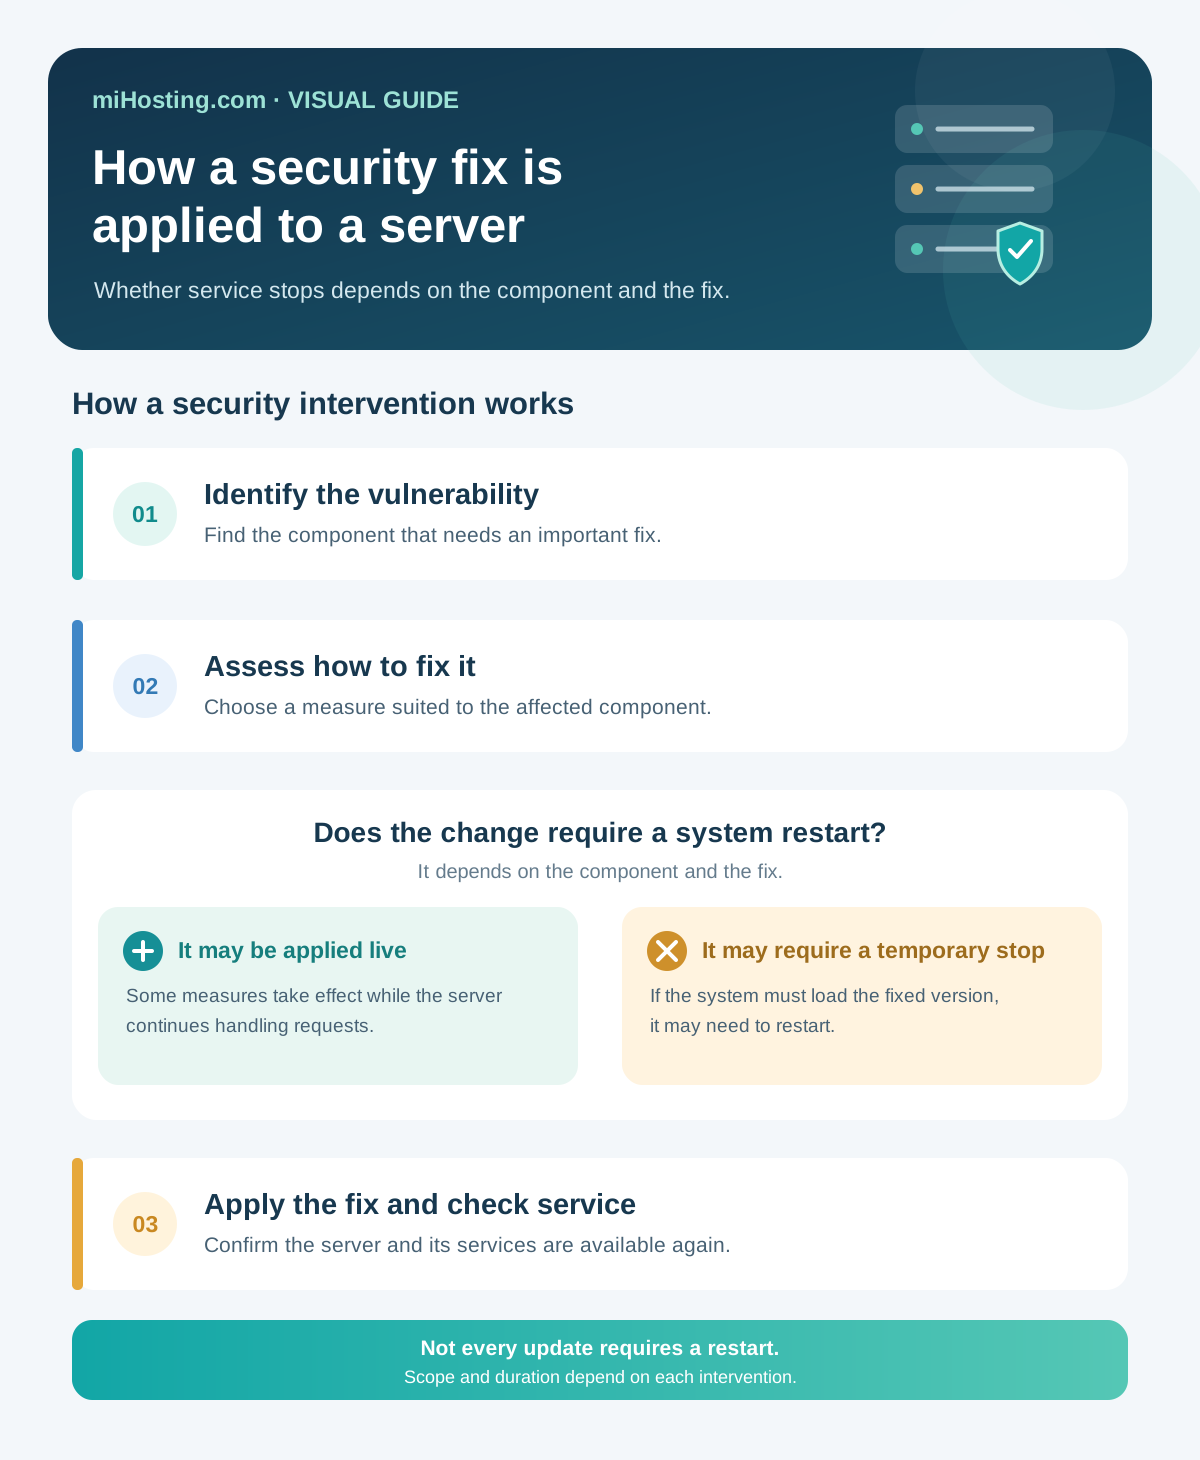
Not every update requires a stop. The decision depends on which component needs fixing and how the change can be applied.
Server security depends on timely action
A vulnerability is a flaw in a program or component that could allow access or activity that should not be possible. When an important issue is identified, the provider must assess its scope and apply the right fix. If the affected component is still running a vulnerable version, installing a fix may not be enough: in some cases, the system has to restart to load the corrected version.
For example, the CloudLinux kernel documentation says that installing certain kernel versions requires a server restart. This is one specific case; it does not mean every security fix requires a restart or that every miHosting intervention affects the kernel.
Why a fix can interrupt service
Some security measures can be applied while the server continues handling requests. Others affect low-level components or require the system to start again before the change takes effect.
When an intervention falls into this second group, keeping the server running can leave the vulnerable version active while the work is completed. Temporarily stopping it allows the fix to be applied and the system to be checked before service resumes.
The impact depends on which server is involved and which services it hosts. A website, email service or application that depends on that server may be unavailable during the intervention.
How artificial intelligence is changing the picture
AI is part of the current cybersecurity landscape. ENISA reports increasing use of these tools by malicious groups to facilitate or improve some of their activities in its Threat Landscape 2026 report. This adds pressure to identify problems and fix them promptly.
ENISA’s 2026 report also records more than 48,000 new vulnerabilities identified in 2025, 22% more than the previous year. That figure counts recorded vulnerabilities: it does not mean cyberattacks increased by 22%, and it does not show that AI caused the rise. Describing the situation as an exponential increase in all security problems would go beyond what the data supports. ENISA summarizes these findings in its press release.
AI is one part of a broader picture. Software flaws, newly identified vulnerabilities and attackers’ techniques are also part of the security work every infrastructure provider must handle.
A temporary interruption to fix an important issue
When miHosting stops a server for security reasons, the aim is to apply the measures needed to fix an important issue. An interruption can be inconvenient, especially if it affects a live website or online store, but delaying a fix can leave the system exposed for longer.
Each intervention depends on the component involved and the available fix. That is why stops can differ in scope and duration.
If you have questions about an intervention affecting your service, contact the miHosting team and tell us which service is affected and when the issue began. Do not include passwords or private keys in your message.
From an idea to your first website.
Try free hosting for 6 months. When you need more resources and support, compare our professional plans. Your domain is purchased separately.